Navigating Verification Protocols Across Automated Charge Networks in Portable Digital Ecosystems
Devon Vogel · Aug 7, 2026
Navigating Verification Protocols Across Automated Charge Networks in Portable Digital Ecosystems
Verification protocols form the backbone of automated charge networks that operate within portable digital ecosystems, where mobile devices handle transactions in real time across wireless connections and cloud-based platforms. Researchers track how these systems combine device authentication, transaction validation, and network security layers to process charges without manual intervention, and data from industry reports shows adoption rates climbing steadily through 2025 into the following year.
Portable digital ecosystems encompass smartphones, tablets, wearables, and embedded IoT sensors that connect to automated charge frameworks, while verification steps confirm identities, authorize amounts, and reconcile records across multiple parties. Observers note that protocols such as EMV 3-D Secure and OAuth-based token exchanges now integrate with device-specific biometrics, and this combination reduces latency during high-volume periods. Studies indicate that by August 2026 several regional networks had rolled out enhanced multi-factor checks that pull data from both hardware and behavioral patterns to flag anomalies before charges complete.
Core Components of Verification in Automated Networks
Automated charge networks rely on layered verification that begins at the device level and extends through gateway servers to settlement systems, and each layer applies distinct checks including cryptographic signatures, certificate pinning, and real-time risk scoring. Those who manage these systems report that portable environments introduce variables such as variable signal strength and frequent handoffs between cell towers or Wi-Fi nodes, yet protocols adapt by caching partial verifications and resuming them once connectivity stabilizes. Evidence suggests that standards bodies continue to refine these mechanisms to maintain consistency across global operators.
One approach involves dynamic token generation that expires after single use, while another employs persistent device fingerprints updated through secure channels, and together these methods support seamless recurring or on-demand charges without repeated user input. Research indicates that integration with portable ecosystems often requires compliance with regional data-protection rules, which in turn shape how verification data travels between endpoints and central ledgers.
Adaptations for Mobile and Wireless Environments
Wireless commerce setups demand verification protocols that function under intermittent connectivity and diverse hardware configurations, so developers embed fallback routines that switch between online and offline modes when signals drop. Figures from regulatory filings reveal that portable devices now account for over sixty percent of automated charges in several markets, prompting networks to prioritize lightweight cryptographic operations that conserve battery life while preserving security margins. Experts have observed that synchronization between local device agents and remote verification servers occurs through encrypted channels that rotate keys at intervals measured in minutes rather than hours.
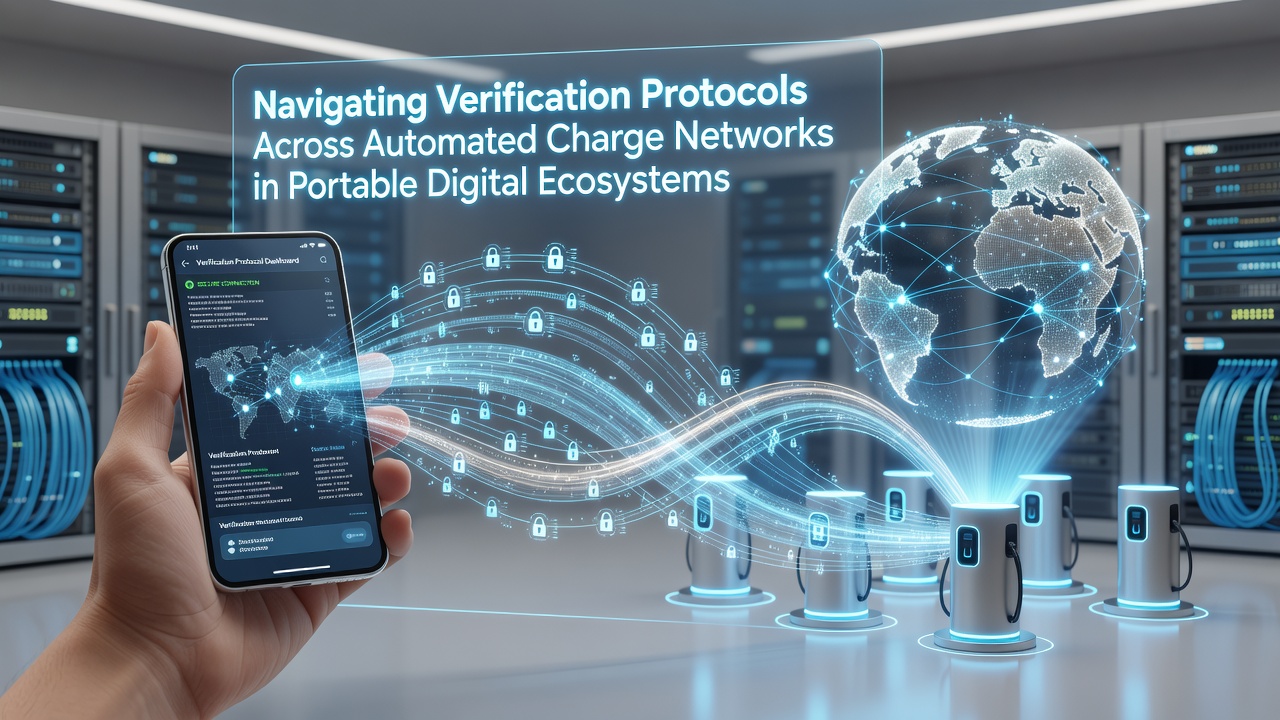
Case examples show merchants deploying portable terminals that query multiple verification sources in parallel, and this parallel querying shortens overall processing windows even when one source experiences temporary delays. Data shows that protocols now incorporate location-based signals alongside traditional identifiers, allowing systems to cross-check whether a charge originates from an expected geographic zone before final authorization.
Recent Developments and Standards Alignment
As of August 2026, updates to verification frameworks aligned portable ecosystems more closely with evolving payment-security specifications, and these updates introduced requirements for continuous monitoring of session integrity throughout the charge cycle. According to NIST cybersecurity guidelines, organizations that implement continuous verification see measurable reductions in unauthorized transaction attempts across distributed networks. Meanwhile, European regulatory updates under PSD2 frameworks have pushed operators to adopt stronger customer authentication methods that portable devices can satisfy through biometric or possession factors without additional hardware.
Industry reports document that cross-border automated charges benefit when verification protocols map local compliance requirements into a unified workflow, and this mapping reduces friction for users who move between jurisdictions. Observers note that testing environments replicate real-world portable conditions, including rapid network switches and variable device states, to validate protocol resilience before broader deployment.
Operational Challenges and Measured Responses
Challenges arise when verification latency compounds across multiple automated charge points, yet networks counter this by prioritizing critical checks and deferring secondary validations until after initial authorization clears. Research indicates that portable ecosystems experience higher rates of device loss or compromise, so protocols incorporate remote-wipe capabilities and revocation lists that propagate within seconds of detection. Those managing large-scale deployments track performance metrics such as verification success rates and retry volumes, and these metrics guide incremental protocol tweaks that maintain throughput without sacrificing accuracy.
One documented instance involved a regional operator that unified verification across several wireless carriers, resulting in streamlined reconciliation processes that cut settlement times by measurable margins. Data from similar implementations shows that combining protocol-level encryption with application-layer monitoring creates overlapping safeguards that address both external threats and internal configuration errors.
Conclusion
Verification protocols continue to evolve alongside automated charge networks in portable digital ecosystems, and ongoing refinements reflect both technological advances and regulatory expectations that differ by region. Evidence gathered through 2026 demonstrates that layered approaches combining device-native capabilities with network-level controls deliver reliable authorization while accommodating the mobility inherent to these environments. Stakeholders track emerging patterns in usage and threat landscapes to adjust verification parameters accordingly, ensuring that automated systems remain functional and secure across expanding digital ecosystems.